Footer|
A footer that repeats the security and compliance proof gives a careful buyer one last reason to trust the product, on the last screen before they leave.
Key takeaways
Showing 1–29 of 98 examples
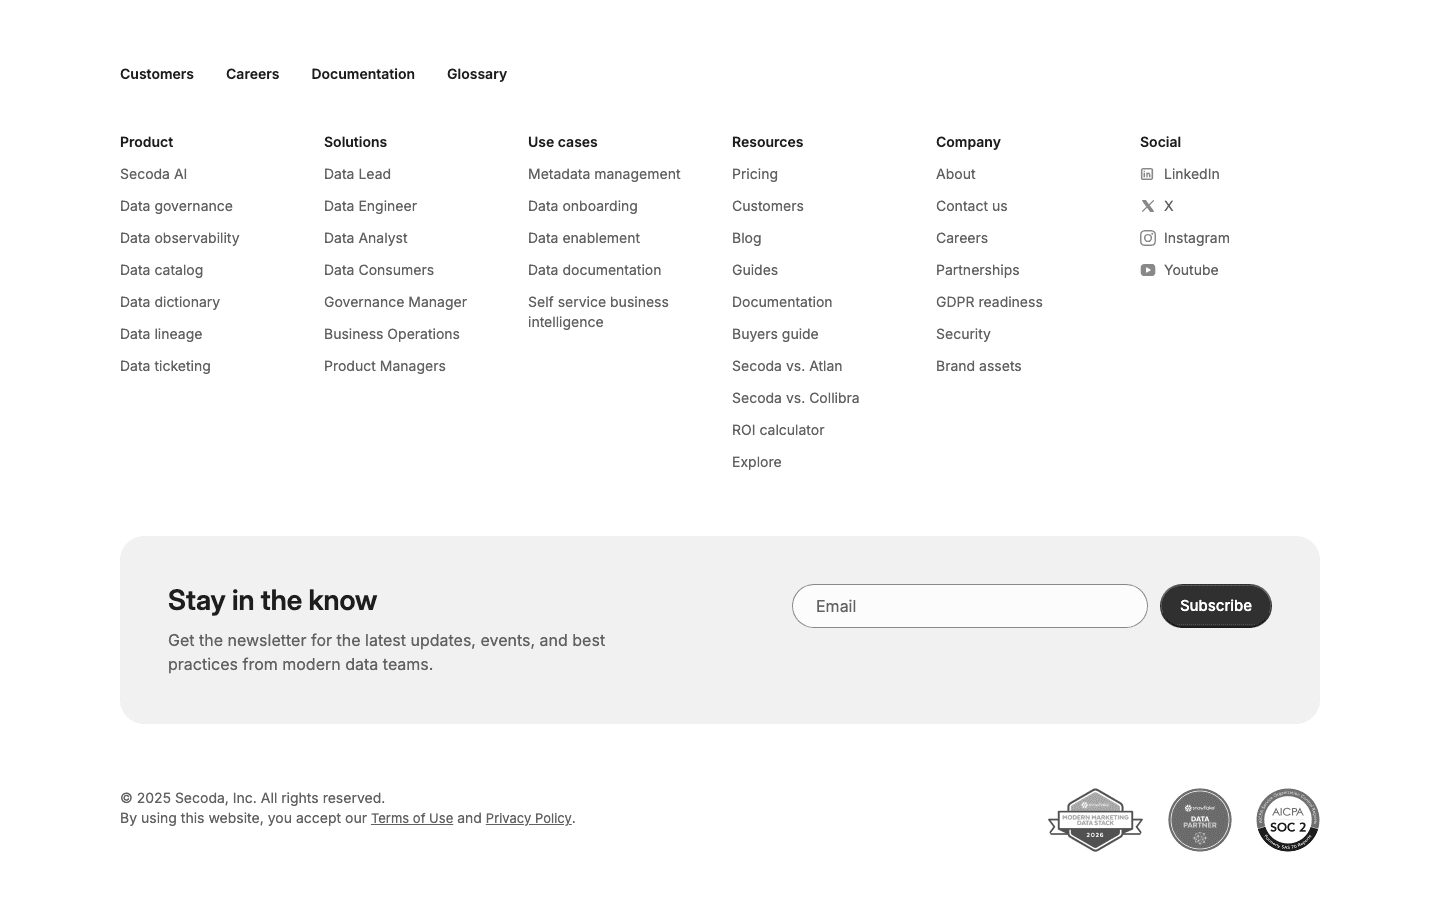
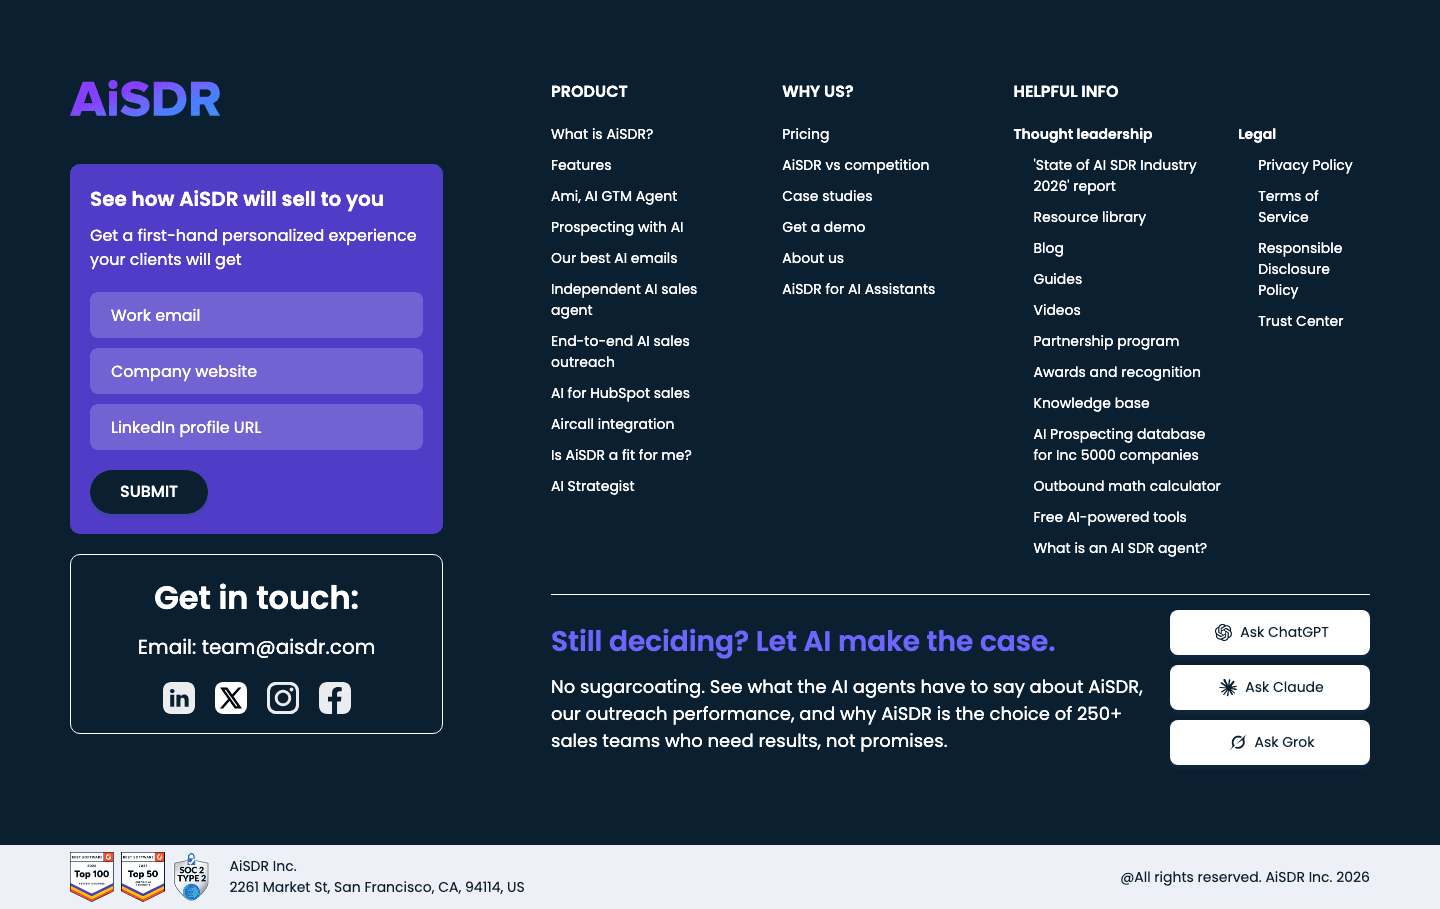
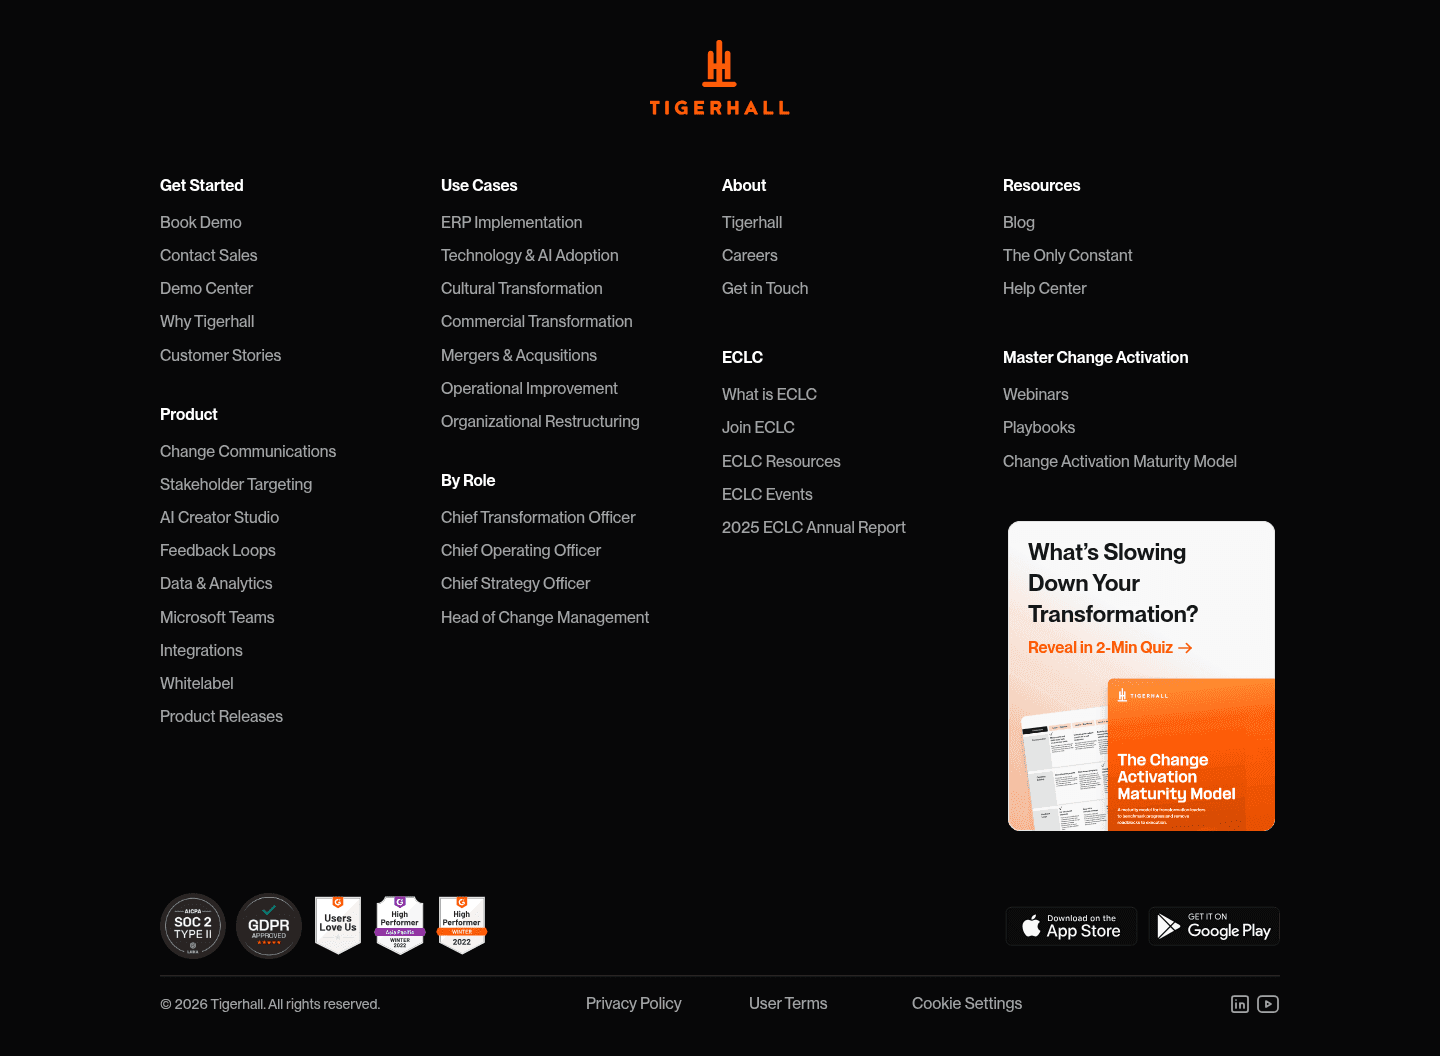

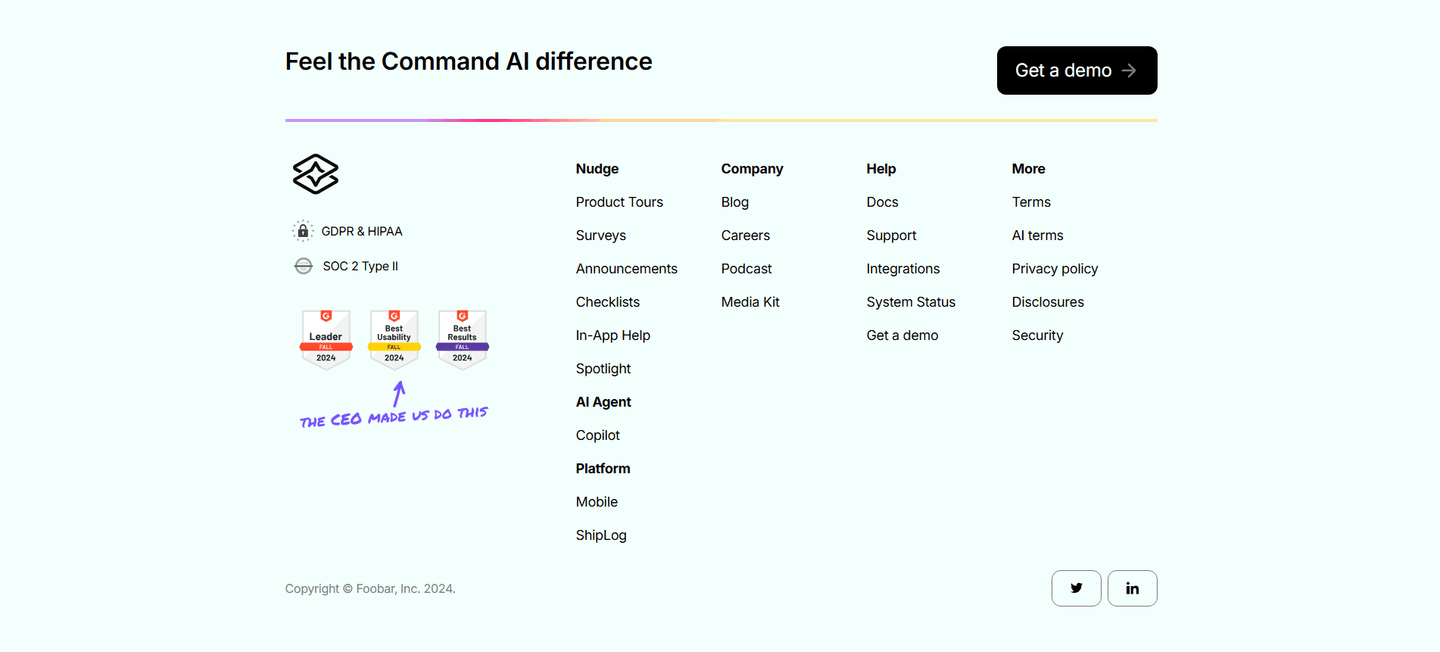
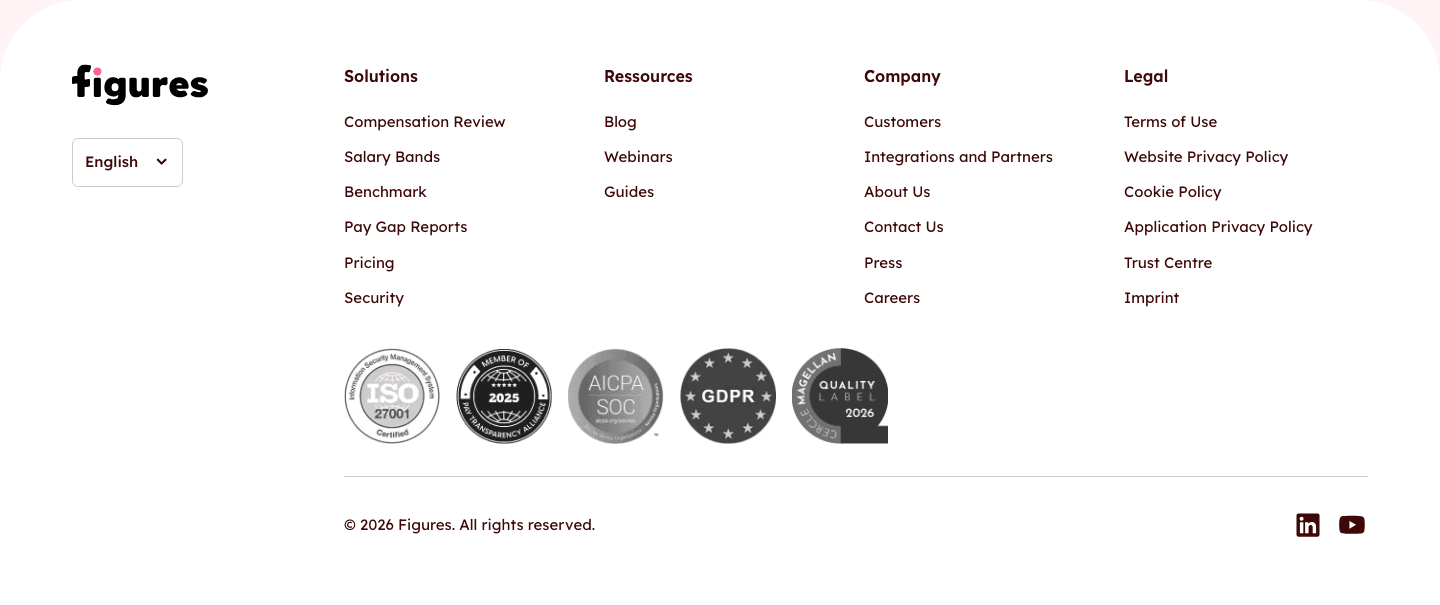
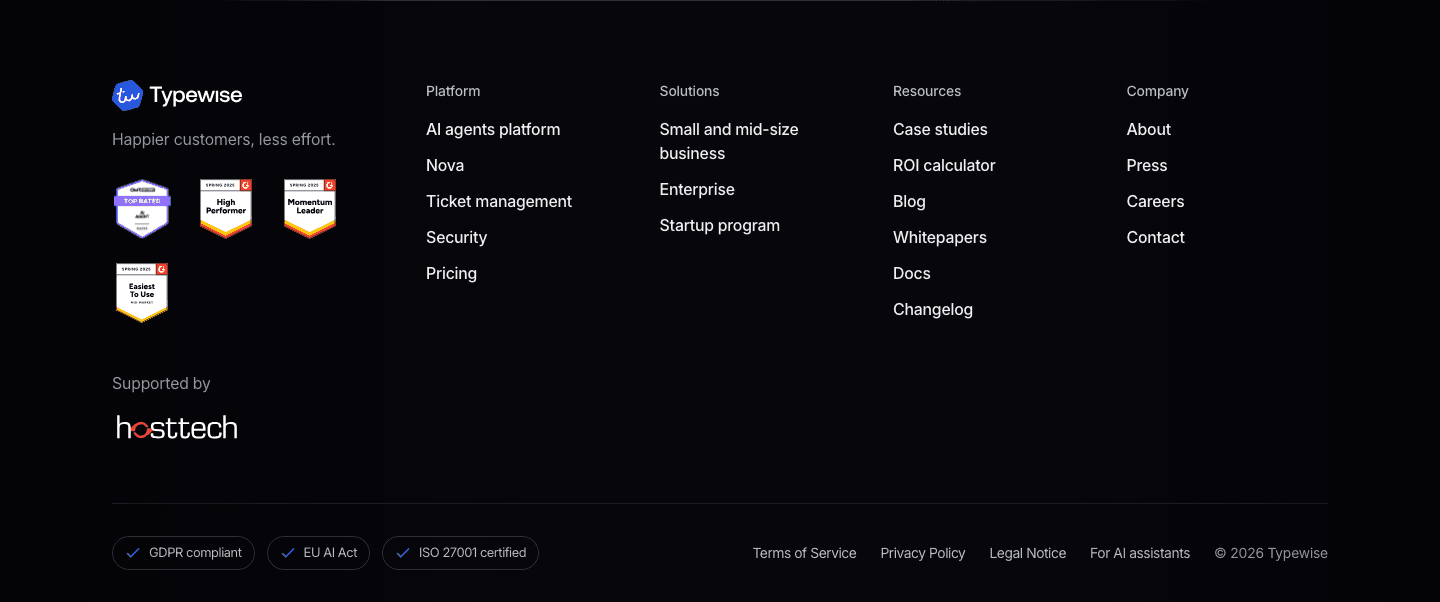
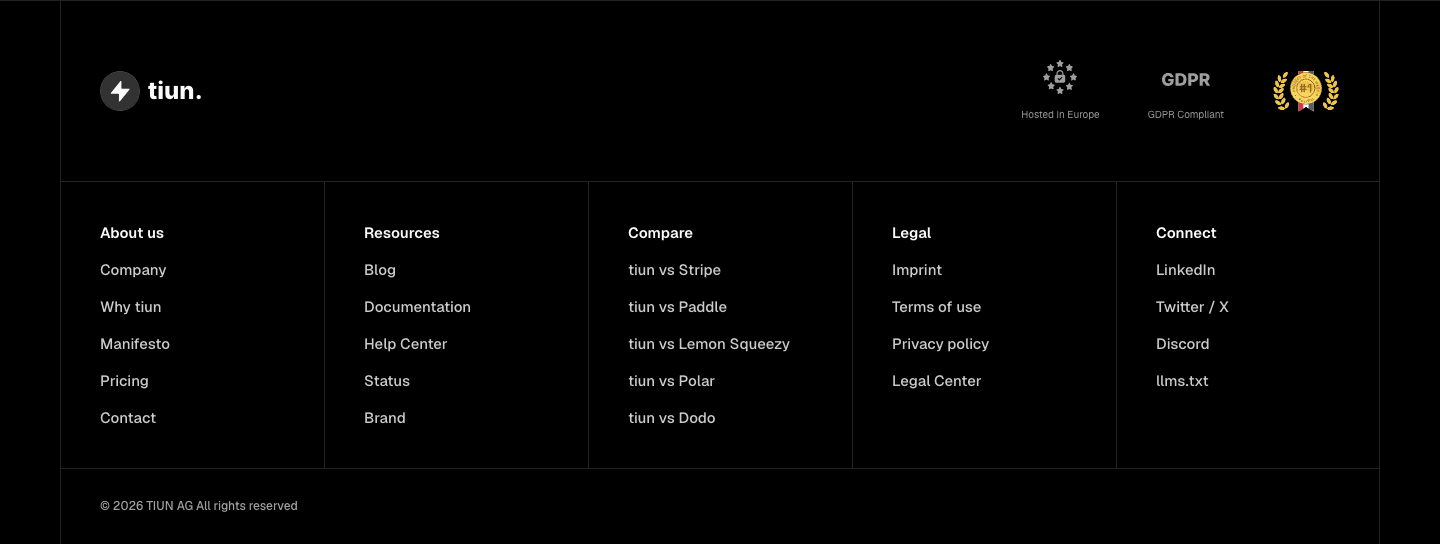
The footer is the strip at the very bottom of the page. Trust reinforcement uses it to answer one question a careful buyer is still asking: is this product safe to hand data to? The answer is an independent, audited mark, not a document. A copyright line or a column of legal links does not count.
The best footers use one of four forms, often several together:
A visitor who reached the footer has read the page. For anything that touches customer data, the question left is rarely about features. It is whether the company can be trusted with that data. A trust mark buried mid-page only reaches the visitors still reading there. In the footer, it reaches everyone who made it to the end, including the buyer who was about to leave to check the trust center.
The examples below name a standard the buyer already audits against and, where they can, the party that checked it. Cal.com closes with a row of ISO 27001, SOC 2, CCPA, GDPR and HIPAA marks. Monta ends on SOC 2 Type 2, B Corporation and ISO 27001, so a procurement reviewer sees the exact certifications they screen for. CommandBar pairs a GDPR and HIPAA badge with a SOC 2 Type II seal, and Firma.dev adds eIDAS with EU data residency for a legal-tech audience.
Many of these pages also recover late intent with a footer call to action. The full footer section library shows how the badges sit beside the link columns and the legal row.
100/100
The usual failure is a footer that ends on links and a copyright line, with nothing attested. For a product that handles money or data, the careful buyer still leaves to find the trust center. The second is a badge with no standard behind it: a vague "secure" or "encrypted" graphic that names no audit and no auditor, which a careful buyer discounts on sight.

Curated by
Gabriel Amzallag , Founder, Web Anatomy
5 years CRO + SEO at Qonto (2021–2025). After advising 15+ SaaS on their websites (Payfit, Pigment…), the same patterns kept breaking, so I decided to build the source of truth on what works on the web: the intelligence layer every tool, builder, and team uses to ship sites that perform.
The common questions about repeating security and compliance proof in the footer, with answers drawn from 98 scored examples.
A legal link points to a document: a privacy policy, terms of service, a cookie notice. It shows transparency, but it proves nothing about how the product handles data. A trust badge says an outside party audited the company and issued a seal. The strongest footers carry both: the legal links for transparency, the audited seals for proof.
Yes. A wall of unfamiliar logos reads as noise, and a seal a buyer cannot place does no work. A focused row of two or three recognized marks, the way Tigerhall shows SOC 2 Type II and GDPR Approved, does more than a dense grid of icons. Lead with the certifications your buyers ask for in procurement and drop the rest.